Vercel
- ISO/IEC 27001:2013
- SOC 2
- PCI DSS
- HIPAA
- GDPR / Data Privacy Framework
- TISAX
Source: vercel.com/security · checked on 2026-09-17
The framework covers the stack end to end. The studio assembles it around your project: every area combines into a single product, delivered fast and built to measure.
We start with the most costly point of friction. The rest only comes once the first building block has proven its worth.
Let's talkThe tool that replaces the shared spreadsheet, double data entry and procedures that only live in one person's head. Designed around how you actually work, not a generic template you have to work around.
Admin interfaces that hold up under daily use: search, bulk editing, roles and permissions, action history, exports. Your teams spend their whole day in them, so they are designed that way.
Chat and voice agents connected to your data and your business actions. They do more than answer: they prepare the work, carry out what can be carried out, and report back.
Your existing tools keep running. We connect them through documented, authenticated APIs instead of rewriting everything, and gradually take over what needs to be taken over.
On request, we test the security of your website or application within an agreed scope. The quote is prepared quickly, and every review ends with findings you can act on.
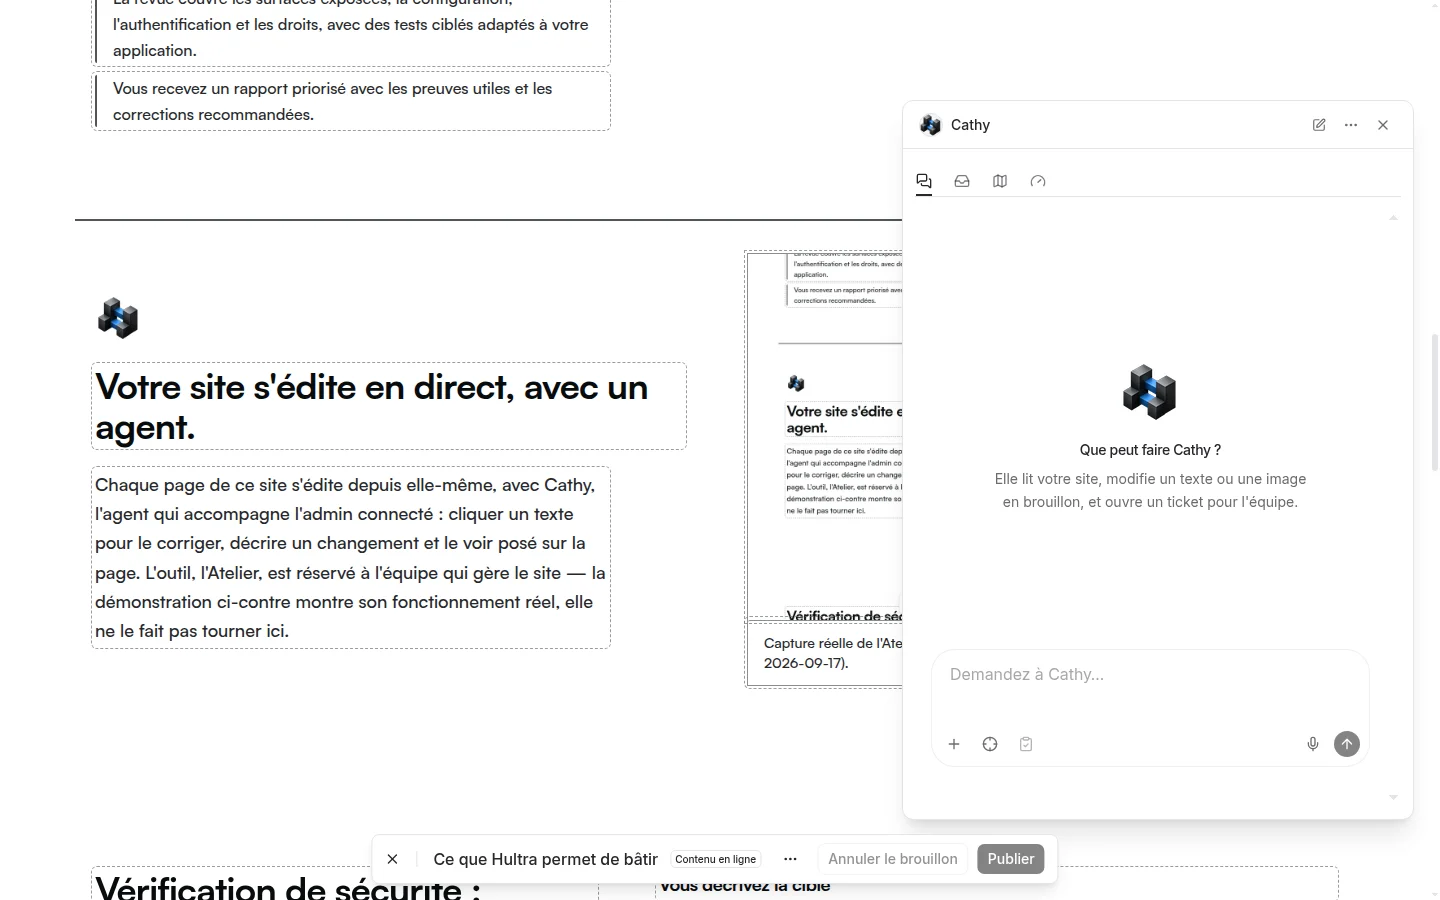
Every page of this site can be edited from the page itself, with Cathy, the agent that works alongside the signed-in admin: click a piece of text to fix it, describe a change and watch it land on the page. The tool, the Atelier, is reserved for the team that runs the site. The demo shown here reflects how it really works; it does not run it here.
A review or a pentest is requested from the contact page. Nothing is tested without a written, authorised scope, and everything ends with a report you can have fixed, by us or by someone else.
From the contact page: the website or application, what worries you, what must not be touched under any circumstances. An address and two lines are enough to get started.
The quote states what will be checked and how (configuration and code review, access checks, targeted tests or a pentest), and what is excluded. You know what you are buying before you say yes.
Targets, limits and terms are authorised in writing before any test. A pentest only takes place on explicit request, within those terms and that scope, never beyond.
Prioritised findings, the relevant evidence, and a recommended fix for each one. It is written to be followed by the team that maintains your tool, whether that is us or not.
Hultra relies on Vercel, Convex and Cloudflare to host, serve and protect your projects. Each one publishes its own attestations: here is what each one actually displays, without crediting anyone with one they do not hold.
Source: vercel.com/security · checked on 2026-09-17
Source: convex.dev/security · checked on 2026-09-17
Source: cloudflare.com/trust-hub · checked on 2026-09-17
Tools change fast in the age of AI. Hultra brings them together for you, and the studio puts them to work on your project. Tell us what you want to build.